Devin adds Mythos deep scans and evidence-backed security patch PRs
3-line summary
- Cognition launched Devin Security 2.0 with Claude Mythos deep scans.
- Enterprise customers are offered free scans and new customers can receive remediation credits.
- Validation settings, human approvals and regional access conditions apply.

Cognition released Devin Security 2.0 on October 26 with Claude Mythos deep scans. Enterprise teams gain managed model access and environment-specific prioritization for proposed fixes.
The company also committed hundreds of millions of dollars in Devin credits. Current and future enterprise customers are offered free deep scans; new customers can receive remediation credits for critical flaws. The announcement gives no per-customer allocation or separate service price.
A threat model built with security and engineering teams guides the work. It maps services, hosts, network policies, data flows and deployment. Staff supply context unavailable from code. Priority depends on an attacker’s access and the damage possible in that environment.
Large scans divide investigation across AI workers. Devin creates rules for selecting relevant code, applies them across source files, investigates bounded batches in parallel, then combines duplicates and related attack paths. This uses an existing execution architecture the company described on July 1.
That earlier technical account places a limit on coverage: files matching no selection rule never reach detailed investigation. Exhausting the selected work queue therefore differs from finding every vulnerability. On repeat runs, the pipeline processes files changed since the previously scanned commit, according to Cognition.
Runtime validation is optional in scan profiles. The product documentation describes isolated application tests returning confirmation, false positives or human-review requests, with logs and screenshots. Normal and deep scans are separate choices; the selected scan and validation settings determine the scope of the results.
Evidence accompanies patches and risk adjustments
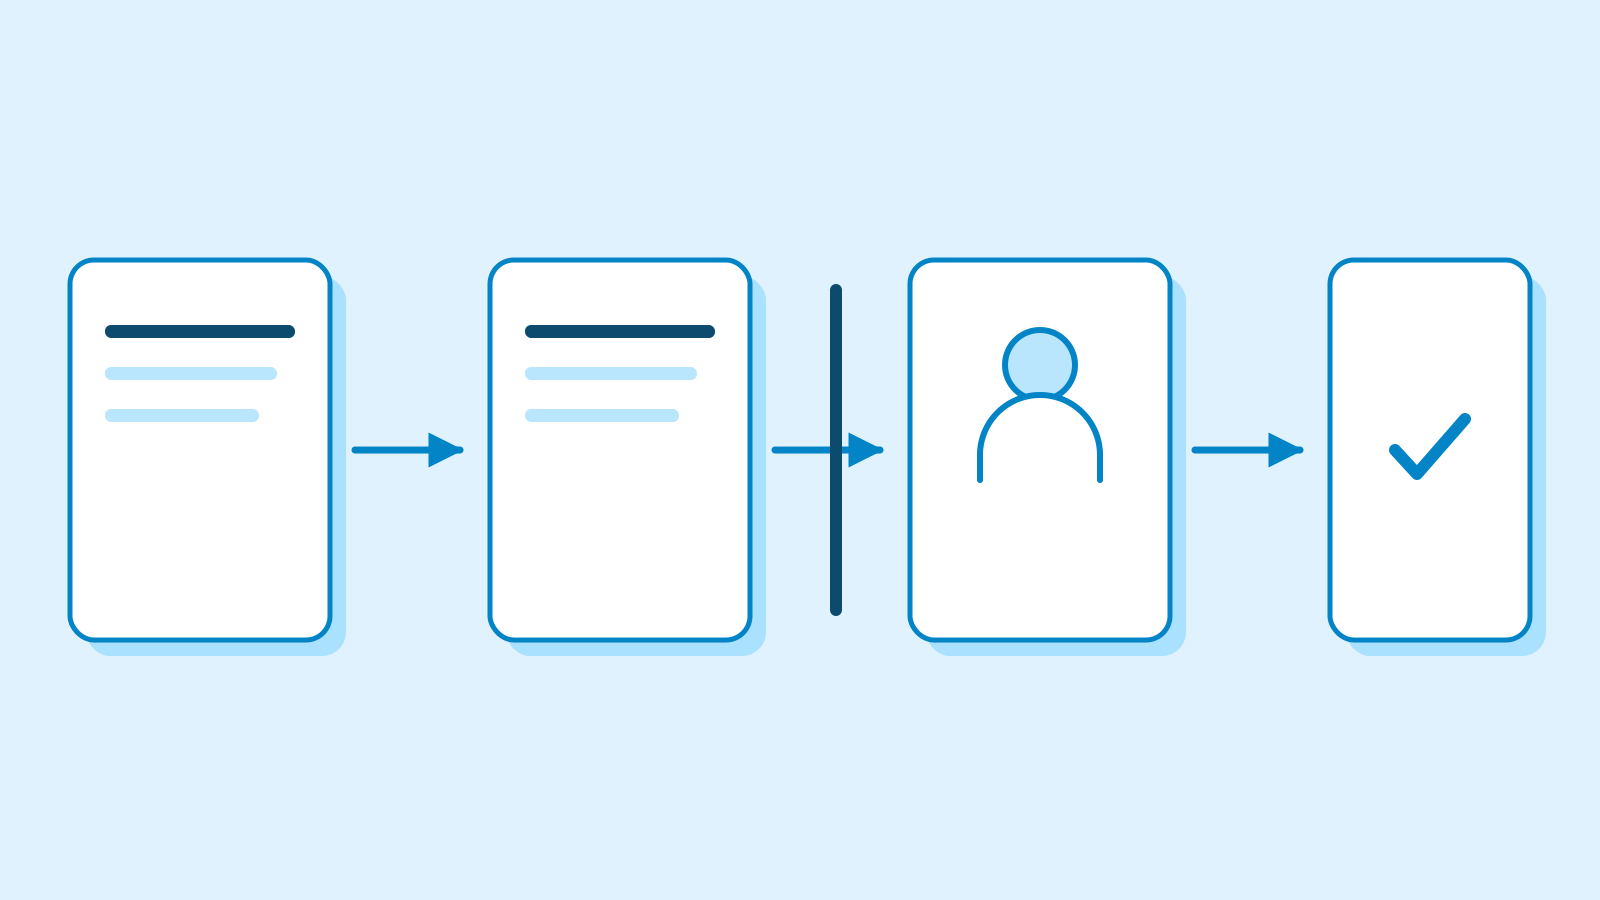
Remediation uses an independent virtual machine for each issue. Devin reproduces and patches the issue, runs reproduction and existing tests, then opens an evidence-backed pull request. The technical post says a finding stays open until the PR merges and Devin verifies the attack path is addressed.
Risk adjustments preserve the original Common Vulnerability Scoring System score. Devin documents reachability, authentication, data and trust boundaries for human approval. It excludes entries in the US Known Exploited Vulnerabilities catalog from relabeling.
Cloud scanning operates under existing service-security terms. The June 11 security document specifies TLS 1.2 or higher for customer data in transit and AES-256 or equivalent protection for stored data under Cognition’s control. Audit logs of material service events are retained for at least a year. It also specifies network separation between development and production, with traffic denied by default and explicitly authorized connections permitted.
The existing data-processing agreement limits customer-data use to service purposes and documented customer instructions. Updated October 21, it requires equivalent training restrictions for subprocessors through contracts or technical configurations. Its customer-data definition covers specified personal data and separates account-administration information.
Features using region-restricted cyber models are enterprise-only, with availability confirmed during contracting. The October 25 supported-region policy lists South Korea, the United States, Japan and the United Kingdom, among others. It governs the restricted-model features rather than the entire Devin Security service.
Personnel of an otherwise supported company can be blocked when physically in an unsupported region. Restrictions also cover entities incorporated or headquartered there, and entities majority-owned or controlled by parties there. Cognition says it may update the list as model providers change availability.
Sources
- Launch and enterprise credits — Cognition
- Security 2.0 workflow — Devin
- Scan modes and validation — Devin
- Execution architecture — July 1 — Devin
- Data-processing terms — October 21 — Cognition
- Restricted-model regions — October 25 — Cognition
- Service-security terms — June 11 — Cognition